Unlike before, compliance is no longer an option for companies to address at the request of a regulator these days. As companies grow, operate in multiple markets, work with third parties and contend with ever-changing regulations, the risk of non-compliance is becoming more difficult to control.
A compliance risk assessment helps companies identify where they could be vulnerable and understand the potential impact and address compliance issues before they become expensive problems. It gives them an opportunity to lay out a strong foundation for effective controls, prudent decision-making and continuing to manage risk of regulatory compliance.
What Is a Compliance Risk Assessment?
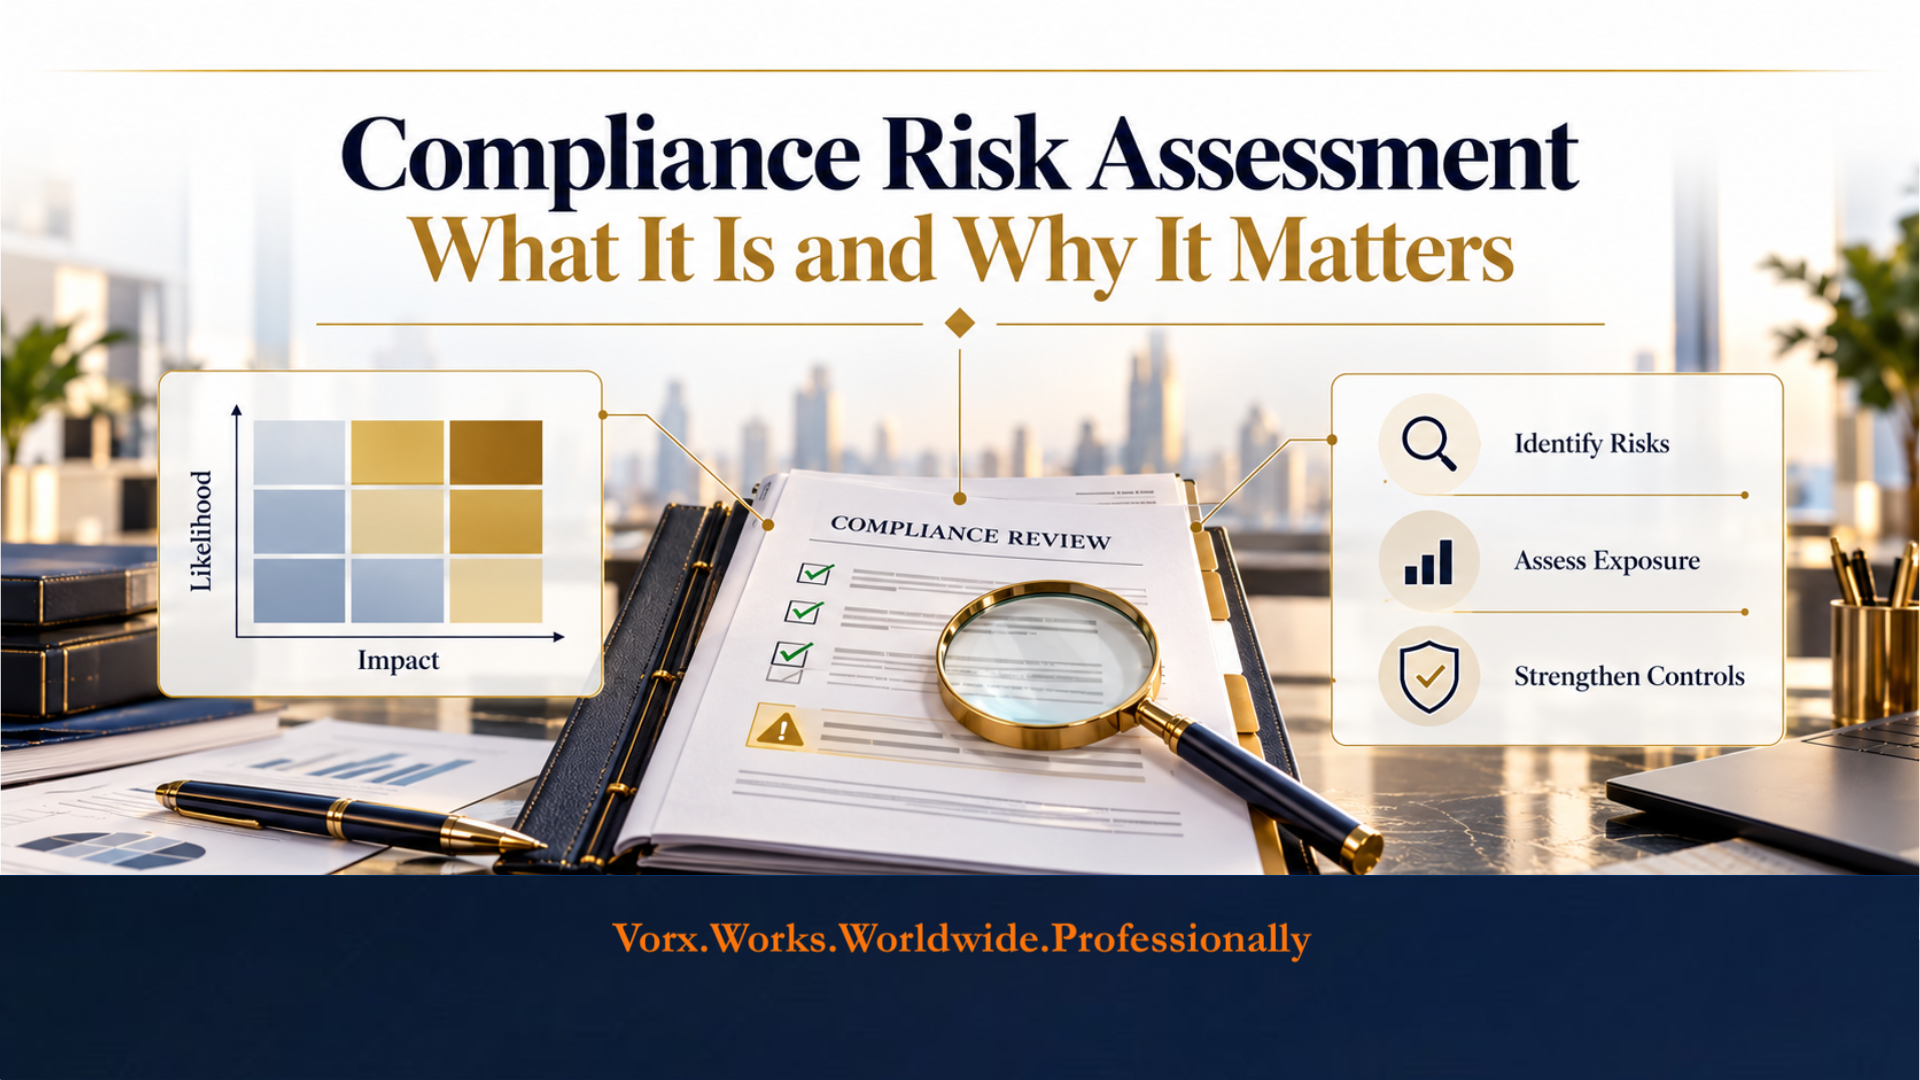
A compliance risk assessment is a structured review to identify and evaluate the likelihood that a business will fail to comply with applicable laws, regulations, contractual obligations or internal policies.
The process generally requires an understanding of the requirements applicable to the business, identification of areas of exposure, evaluation of the likelihood and impact of those risks and determination of whether existing controls are adequate. For businesses operating internationally, a regulatory compliance risk assessment can be particularly important because requirements may differ in jurisdictions, industries and business activities.
Explore the right jurisdiction for your business with Vorx Consultancy. Visit Vorx Consultancy
What Are the Key Benefits of a Compliance Risk Assessment?
A well-designed assessment can provide several practical benefits:
Early risk identification: Potential compliance issues can be identified before they escalate.
Better prioritisation: Management can focus attention on higher-impact risks.
Stronger controls: Policies and procedures can be tested for effectiveness.
Improved accountability: Responsibilities for addressing compliance gaps are clearer.
Greater preparedness: Businesses are better prepared to respond to regulatory changes or reviews.
These are some of the core compliance risk assessment benefits that make regular assessment valuable beyond simple regulatory compliance.
What Does a Compliance Risk Assessment Cover?
The exact scope depends on the business, industry and jurisdictions involved. A typical corporate compliance risk assessment may review the following areas:
Area | What May Be Reviewed |
Regulatory | Applicable laws, licences and reporting |
Financial | Tax, financial controls and record keeping |
Operational | Policies, processes and employee practices |
Data | Privacy, security and data-handling requirements |
Third Parties | Vendors, suppliers and external partners |
This scope can be expanded depending on the company’s activities and regulatory exposure. The objective is effective compliance risk identification, rather than creating an unnecessarily large checklist.
Explore the right jurisdiction for your business with Vorx Consultancy. Visit Vorx Consultancy
When Should a Compliance Risk Assessment Be Conducted?
A compliance assessment should not necessarily be treated as a one-time exercise. Regular compliance risk monitoring helps businesses identify new risks as their operations and regulatory environment change. An assessment may also be appropriate when:
- Entering a new country or market
- Launching a new product or service
- Undergoing a major organisational change
- New regulations affect the business
- A significant compliance incident occurs
- Working with new high-risk third parties
Regular reviews help ensure that the assessment remains relevant as the business develops.
Recommended Reading:
A proper International Tax Planning can also help companies understand and manage tax-related compliance risks across jurisdictions.
How to Conduct a Compliance Risk Assessment?
A compliance risk assessment should follow a structured process so that risks are identified, evaluated and converted into clear corrective actions. The exact approach may vary by industry and jurisdiction, but the core process generally includes the following steps:
- Identify Applicable Compliance Requirements
Start by mapping the laws, regulations, licences, contractual obligations and internal policies relevant to the business. For companies operating internationally, requirements should be reviewed separately for each jurisdiction and business activity. - Identify Potential Compliance Risks
Review business activities, processes and existing practices to determine where the company could fail to meet its obligations. This may include gaps in reporting, licensing, tax, data handling, documentation or internal procedures. - Assess Likelihood and Impact
Each identified risk should be evaluated based on two key factors: how likely it is to occur and how serious the consequences could be. This provides a basis for consistent compliance risk analysis and prioritisation. - Evaluate Existing Controls
Review the policies, procedures and controls already in place. The focus should not only be on whether a policy exists, but whether it is properly implemented, documented and effective in reducing the identified risk. - Prioritise Compliance Gaps
Once risks and control weaknesses are assessed, classify them according to their potential impact and urgency. High-priority issues should receive immediate attention, while lower-risk matters can be addressed through planned monitoring and remediation. - Create and Monitor an Action Plan
For each significant gap, define the corrective action, responsible person or team and expected timeline. The assessment should then be reviewed periodically to track remediation and identify new risks arising from regulatory or business changes.
Explore the right jurisdiction for your business with Vorx Consultancy. Visit Vorx Consultancy
How Are Compliance Risks Prioritized?
Not every compliance risk requires the same level of attention. A basic compliance risk assessment framework can classify risks according to their likelihood and potential impact.
Risk Level | Recommended Approach |
High | Address immediately and assign clear ownership |
Medium | Create a defined remediation plan |
Low | Monitor and review periodically |
This prioritisation helps businesses allocate resources where they can have the greatest impact and supports a more effective compliance risk management framework.
Recommended Reading:
For companies operating globally, Compliance Requirements for International Businesses highlights key obligations that should be considered during a compliance risk assessment.
Common Challenges in Compliance Risk Assessment
A compliance risk assessment can become difficult when a business has multiple entities, jurisdictions, regulations or internal processes to review. The challenge is not only identifying risks, but also determining which risks are relevant and what action should follow. Some common challenges include:
- Mapping the right requirements: Businesses may struggle to determine which laws, licences, regulations and reporting obligations actually apply to their activities.
- Measuring risk consistently: Different teams may assess the same risk differently, making it difficult to assign a consistent risk rating.
- Finding control gaps: A company may have policies in place but lack evidence that those controls are working effectively in practice.
- Handling cross-border requirements: International businesses may need to assess overlapping requirements across multiple jurisdictions.
- Prioritising remediation: Identifying several risks does not automatically show which issue should be addressed first or how quickly it requires action.
How Vorx Consultancy Helps With Compliance Risk Assessment?
The regulatory environment is constantly changing; therefore, there is a need for companies to stay updated on these developments to have reliable processes and adequate controls in place. Vorx Consultancy offers expert international tax and corporate consulting to help multinational corporations identify and leverage key strategic opportunities in their target markets while also advising on local regulatory compliance and control requirements.
Vorx Consultancy’s compliance risk assessment experts can assist businesses in learning what to do or help them prepare documentation for regulatory authorities to demonstrate that controls are robust enough to prevent or detect violations.
Get expert compliance risk assessment support from Vorx Consultancy.
Book a Strategy Call: (Calendly Link)
Visit: www.vorxcon.com
Email: support@vorxcon.com
Final Thought
A compliance risk assessment enables organizations to identify the likelihood of violating internal controls or regulations. It is at this juncture that businesses can decide what should be done about the risks that serve as a basis for developing effective mitigation strategies.
Regulatory and business compliance plans are perpetually subject to alterations and modifications; hence, business compliance risk assessment becomes indispensable to ensure that the initiatives support a robust compliance program. Companies must be in a position to respond accordingly to prevent penalties or reputational damage. Entities that operate in more than one region ought to invest in a regulatory compliance risk assessment to assist them in keeping up with new rules and regulations governing their operations.
